
Cloud services can provide strong security capabilities, but moving a workload does not make it secure by default. The practical benefit depends on the service chosen, the settings the customer controls, and whether someone reviews alerts, access, backups, and recovery.
Understanding Cloud Services and Cybersecurity
Cloud services are broadly categorized into three main types: Infrastructure as a Service (IaaS), Platform as a Service (PaaS), and Software as a Service (SaaS). Each of these services offers unique features and capabilities:
- IaaS provides virtualized computing resources over the internet, allowing organizations to scale their infrastructure as needed.
- PaaS offers a platform for developing, testing, and deploying applications without worrying about the underlying infrastructure.
- SaaS delivers software applications over the internet, eliminating the need for local installations and updates.
While cloud services offer numerous benefits, they also introduce new cybersecurity concerns. These include data breaches, unauthorized access, and challenges related to compliance with industry regulations such as GDPR and HIPAA. For example, cloud environments often involve multiple users and shared resources, increasing the potential for security lapses if access controls are not properly configured.
Cloud services differ from traditional security approaches in several ways. In traditional on-premises environments, companies are solely responsible for managing hardware, software, and security measures. In contrast, cloud services operate on a shared responsibility model. This means that while cloud providers ensure the security of the cloud infrastructure, customers are responsible for securing their data, applications, and access permissions within the cloud environment. Understanding this distinction is crucial for effectively using cloud services to enhance cybersecurity.

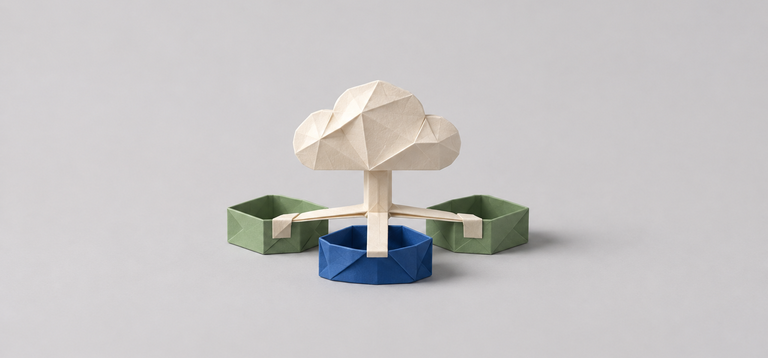
Conceptual model: Simplified responsibility model: provider infrastructure and customer access and data.
Key Benefits of Using Cloud Services for Cybersecurity
Cloud services offer several advantages that make them a compelling option for organizations looking to strengthen their cybersecurity posture.
Scalability and Flexibility
Cloud services provide the ability to scale resources up or down based on demand. This is especially valuable for cybersecurity, as organizations can allocate additional resources during periods of heightened threat activity. Scalability also enables companies to implement complex security measures, such as advanced threat detection systems, without investing in additional hardware.
Centralized Security Management
One of the key benefits of cloud services is the ability to centralize security management. This means that security policies and protocols can be enforced consistently across the organization from a single cloud-based console. Centralized management also simplifies monitoring and auditing, making it easier to detect and respond to potential security issues.
Cost Efficiency
Adopting cloud services can lead to significant cost savings. Providers maintain the infrastructure within their responsibility. Customers may still need to patch guest operating systems and applications, manage identities, review logs, and pay for security services and expertise. organizations can avoid the upfront capital expenditures associated with traditional security infrastructure.
Real-Time Threat Monitoring and Response
Cloud providers use advanced technologies such as artificial intelligence (AI) and machine learning to offer real-time threat monitoring and response capabilities. These systems analyze vast amounts of data to identify unusual patterns and potential security threats. Automated alerts and responses enable organizations to mitigate risks quickly and efficiently.
Compliance and Regulatory Support
Cloud providers often offer pre-built compliance frameworks to help organizations meet industry regulations such as GDPR, HIPAA, and PCI-DSS. A provider’s assurance reports and tools can support an assessment, but the customer must still evaluate their workload, contracts, data flows, and applicable obligations. Buying a service does not confer automatic compliance.
Cloud Security Tools and Features
Cloud platforms offer a comprehensive suite of security tools and features aimed at bolstering cybersecurity defenses. Some of the most critical tools include.
Data Encryption
Data encryption, whether at rest or in transit, is a cornerstone of cloud security. By encrypting data, cloud providers ensure that even if information is intercepted or accessed by unauthorized individuals, it remains unintelligible without the correct decryption keys.
Identity and Access Management (IAM)
IAM tools, such as multi-factor authentication (MFA), single sign-on (SSO), and role-based access control (RBAC), are designed to regulate user access to sensitive data and applications. These solutions provide detailed control over who can interact with specific resources, helping restrict access according to configured identity and authorization rules and minimizing the chances of unauthorized entry.

Illustrative example: Security key, storage box, and padlock illustrate identity and data controls.
Cloud Firewalls and Security Groups
Cloud firewalls and security groups serve as protective barriers that manage network-level security. They filter both inbound and outbound traffic, filtering connections according to configured rules and supporting network segmentation to protect sensitive resources.
Intrusion Detection and Prevention Systems (IDPS)
IDPS solutions employ automated technologies to identify and counter malicious activities within cloud environments. By monitoring traffic patterns and analyzing anomalies, these systems can quickly detect potential threats and take preventive measures to isolate or block harmful actions before they cause damage.
Overcoming Challenges of Cloud Security Implementation
While cloud services offer numerous security benefits, implementing them effectively can be challenging. Organizations must address several key issues.
Data Ownership and Privacy Concerns
One common concern is data ownership and privacy. When data is stored in the cloud, organizations must ensure that it remains under their control and is not accessed or used by unauthorized parties. Implementing robust encryption and access controls can mitigate this risk.
Shared Responsibility Model
Understanding the shared responsibility model is critical. Cloud providers are responsible for securing the cloud infrastructure, but customers must secure their data and applications within the cloud. Organizations should establish clear policies and procedures to address their security responsibilities.
Cloud Misconfiguration Risks
Misconfigured cloud environments are a leading cause of data breaches. Organizations should use automated configuration management tools and conduct regular security audits to ensure their cloud settings are correctly configured and compliant with security best practices.
Wrapping Up
Cloud services have emerged as a powerful tool for enhancing cybersecurity. Their scalability, real-time monitoring capabilities, and compliance support make them an attractive option for organizations of all sizes. By using the advanced security features offered by cloud providers, companies can build a robust security framework that is both cost-effective and capable of responding to evolving threats.
To maximize the benefits of cloud-based cybersecurity, organizations must understand the shared responsibility model, implement strong access controls, and continuously monitor their cloud environments for potential misconfigurations and vulnerabilities. With the right strategy in place, cloud services can become a cornerstone of a comprehensive cybersecurity strategy, helping organizations protect their most valuable digital assets.
As the digital landscape continues to evolve, cloud services will play an increasingly vital role in safeguarding businesses against cyber threats. Organizations should consider adopting cloud solutions as part of their long-term cybersecurity strategy, enabling them to stay ahead of emerging threats and secure their digital future.
Assign controls to named owners
Make a responsibility table for identity, host patching, application updates, encryption keys, network rules, logs, and backups. Confirm the boundary for each service rather than copying one IaaS model onto a SaaS product. Use least privilege, test restoration, and review whether an alert actually reaches an on-call person.
The AWS shared-responsibility model shows why customer duties vary with the service. In a marketing team, also inventory access to publishing tools and remove departed staff promptly. SU Social’s Drafts tab can hold public security education for editing; it should not become a repository for credentials or incident evidence.
Meet the Author
Ichiro Satō is a seasoned cybersecurity expert with over a decade of experience in the field. He specializes in risk management, data protection, and network security. His work involves designing and implementing security protocols for Fortune 500 companies. In addition to his professional pursuits, Ichiro is an avid writer and speaker, passionately sharing his expertise and insights on the evolving cybersecurity landscape in various industry journals and at international conferences.
Leave a Reply